Subscribe

Get our E-Mail Newsletter:


Lastest posts

Blogrolls
My Facebook


 Opera Mini for iPhone submitted to Apple for approval


Opera Mini for iPhone was officially submitted to the Apple iPhone App store today. A select few first saw it at Mobile World Congress 2010 in February. Now, the “fast like a rocket” browser is taking its first big step towards giving users a new way to browse on the iPhone.

Early reviews of Opera Mini for iPhone praised the sheer browsing speed, powering through Web pages up to six times faster than Safari. Due to server-side rendering, Opera Mini compresses data by up to 90 percent before sending it to the phone, resulting in rapid page loading and more Web per MB for the end user. Those familiar with iPhone roaming charges will relish Opera Mini’s ability to deliver more for less, giving users the Web they want quickly, without, the high costs.


“The Opera Mini for iPhone sneak peek during MWC told us that we have something special,” said Jon von Tetzchner, Co-founder, Opera Software. “Opera has put every effort into creating a customized, stylized, feature-rich and highly responsive browser that masterfully combines iPhone capabilities with Opera’s renowned Web experience, and the result is a high performing browser for the iPhone.”

Opera Mini is the world’s most popular mobile Web browser, famed for bringing the Web to nearly any mobile phone. Its speed, usability and navigation-friendly design have catapulted this browser onto more than 50 million mobile phones worldwide. Creating a version for iPhone is part of Opera’s mission to bring the Web to all platforms and all devices.

Labels: ,

Read more...

 Star Defense Strategic Tower Placement Video


The Star Defense release date has to be drawing near, we can feel it. We have been getting fed a regular dose of screenshots and gameplay videos for some time now, but we still have no official release date for this highly anticipated tower defense game. To tide you over for just a little while longer, ngmoco has released a brand new Star Defense strategic tower placement video.

The latest Star Defense gameplay video embedded below shows players how to strategically place towers to successfully defend against waves of the incoming S’rath aliens. The video is narrated by ngmoco’s Mary Jane Irwin.

Hopefully the next time we have something to say about Star Defense, it will include a release date and price. Cross your fingers!

Labels: ,

Read more...

 Hit The Streets Of New York In TaxiDrive


We have seen a recent surge of big, time consuming games for the iPhone like The Sims 3 and Return to Mysterious Island. They are great games in their own right, but the iPhone is a mobile device after all and sometimes we just want to play a quick casual game while on-the-go. Conveniently, Steffen from syncRage has informed us about their new casual game TaxiDrive that should help you waste some of those extra seconds you may have.


TaxiDrive is a simple casual game that requires you to hit the streets of New York in your taxi cab in an attempt to generate as much income as possible. The game uses a top-down perspective to help you easily navigate the streets. You must head to all corners of the city to pick up and then drop off your passengers. TaxiDrive allows you to control your taxi two different ways: one being a tap and drag method that allows you to control the path of your taxi instantly, and the other is a single tap control that chooses the best route for you. You will have to constantly alter the path of your taxi to avoid the traffic because as the game progresses, the traffic picks up.

TaxiDrive features three unlockable maps with demanding challenges, the ability to gain more taxis to extend the game by wracking up cash, and a local high score list. The developers intend on issuing an update very soon that will add more maps.

TaxiDrive is available in the App Store for the introductory price of $.99.

Labels: ,

Read more...

 X-SIM II for iPhone


All new iPhones being sold in the US, UK & Germany are locked to a particular provider (Version 1.1.2, Bootloader 4.6)

If you wish to use the iPhone with another provider in that country or in another country, you will need the X-Sim II to ypass the lock to work with your exising sim card. In Canada, it will work with Rogers & Fido Networks.
X-SIM II for iPhone

Also works with: at&t, T-Mobile, Vodaphone, ORANGE, Mobile , o2, Tesco, CosmOTE, Tim & Virgin.

And please alert that that's not the exact solution of unlocking the phone, it's BY- PASS the SIM checking of the phone. For example, there is an locked AT &
T iphone, and of course, else of AT & T SIM card, the phone cannot work on any card else. So, when the user want to use the own card, it needs to put the own card into that X-SIM II card slot, then, put to the iphone. When iphone detect the
card, that X-SIM II would BY-PASS the checking to determine if there is AT & T or not, then, the iphone would still work with the user's own card.

So, the conclusion is that the iphone is not really unlocked, it just BY-PASS the SIM checking & let the iphone to work on any SIM card. Just Jailbreak the iPhone, update it, Jailbreak it again, insert your Sim card together with the X-Sim II, & you phone features will work on your iPhone. Very simple to do & you can not damage your phone!!! X-Sim II requires no modification of the basebandon your phone.

Labels: ,

Read more...

 For Apple iPhone, Japan Could Be the Next Big Test


Apple Inc. may be close to the most important test yet of its iPhone's global appeal.

Apple Chief Executive Steve Jobs recently met with officials from Japan's dominant mobile operator, NTT DoCoMo Inc., including NTT's president, Masao Nakamura, to discuss a deal to offer the iPhone in the country, say people familiar with the situation. These people say Apple has also been talking to Japan's No. 3 operator, Softbank Corp. Executives from both NTT and Softbank have also made multiple trips to Apple's Cupertino, Calif., headquarters.

In Japan, one of the world's largest and most demanding mobile-phone markets, Apple will face ferocious competition from other handset makers. Indeed, it will be joining a long list of foreign phone makers that have tried to break into the insular Japanese handset market, most with little success. It also remains to be seen whether a top Japanese carrier will accept Apple's unusually tight control over the design of the iPhone.

Representatives at Apple, DoCoMo and Softbank declined to comment.

Success in Japan is crucial if Apple is to keep up the momentum of a product that has sold well but not quite as well as some Wall Street analysts initially forecast. Since its launch in late June, the iPhone has been one of the top-selling smart phones in the U.S., where it is sold through AT&T Inc., the nation's largest carrier based on number of subscribers. More recently, the product went on sale with carrier partners in the U.K., France and Germany, where Piper Jaffray & Co. analyst Gene Munster believes its sales have been "good, but not over-the-top good."

Reaching agreement with a wireless partner in Japan soon is an important step toward Apple's oft-stated goal of gaining 1% of the global cellphone business by the end of 2008. That would mean it would have to ship some 10 million iPhones, a goal Mr. Munster and many other analysts now believe Apple will exceed. Through late September, Apple says, it sold a total of 1.4 million iPhones. Mr. Munster predicts that 15% of iPhone sales next year could come from Japan, placing that country behind only the U.S. and the U.K.

Japan, the world's second-largest economy after the U.S., is an attractive market for Apple. The company has long had a strong brand there through its Macintosh computers and iPod products. It also has seven retail stores there -- one of its largest presences overseas -- including a flagship store in Tokyo's Ginza shopping district that is often jammed with gadget lovers.

What's more, Japan's nearly 100 million mobile-phone users buy new phones every two years on average. And Japanese consumers are already used to shelling out hundreds of dollars for expensive phones with advanced features such as digital TV, music and a camera.

Apple has said it will launch the iPhone in Asia sometime next year. The iPhone that Apple will ship in Japan is likely to be a new version that supports "3G" networks, which provide far faster Internet surfing speeds. Analysts expect that device to be available by the middle of next year. The current iPhone wouldn't work in Japan, where older networks are based on a different technology standard than the rest of the world.

Still, Japan will be a difficult market for Apple to crack. More than 10 domestic mobile-phone makers work closely with the three major operators there to develop phones that cater to Japanese consumers' tastes. While the market share of foreign manufacturers has been rising slowly, they make up only about 10% of Japan's annual phone sales of about 45 million to 50 million units, according to Yano Research Institute. Sharp Corp. was Japan's dominant mobile manufacturer with a 26.2% market share in the April-to-September period, according to Japanese market research firm MM Research Institute.

And though Apple's iPod music devices are popular in Japan, they have faced competition. Sony Corp. has made a small dent in Apple's share with its Walkman music players, as have Japanese mobile-phone makers, which equip their models with sophisticated iTunes-like music features. Many Japanese consumers already purchase and download music over their current mobile phones.

Apple has nearly 50% of Japan's digital music-player market, according to industry data, but that's smaller than the roughly 70% share it has in the U.S. In the Japanese market, where each mobile operator refreshes its lineup twice a year with the latest phone models, packing them with advanced technology and features, the Apple iPhone will have to keep pace.

Still, Yasumasa Goda, a telecom analyst at Merrill Lynch & Co., says Apple could do quite well in Japan. "Apple and iPod are already established brands in Japan, so they're starting from a different place than other foreign manufacturers," he says.

Richard Doherty, an analyst at the electronics research firm Envisioneering Group in Seaford, N.Y., says he saw excitement about the iPhone in Japan firsthand in October. He was attending a technology conference and was mobbed by executives from electronics and wireless companies who wanted to see his Apple phone. "It attracted crowds everywhere," he says.

In Japan, Softbank has been widely believed to be interested in partnering with Apple. But people familiar with the matter say DoCoMo is likely to be Apple's first choice because of the strong preference the U.S. company has shown so far for signing agreements with top mobile operators.

The two sides are still negotiating terms, these people say. One sticking point is the share of subscriber revenue that Apple is demanding. People familiar with the situation say Apple is asking for a percentage of revenue that is comparable with what it receives from other carriers. Some analyst estimates put that figure between 10% and 20%. If it can't reach a deal with DoCoMo, Apple may turn to Softbank, which has been making an aggressive push to take customers away from its larger rivals. A person familiar with the situation says Apple doesn't expect to have any difficulty concluding a deal with a Japanese operator.


 For Apple iPhone,
 For Apple iPhone,
source

Labels: ,

Read more...

 Free Version of Navizon GPS for iPhone Now Available


Free Version of Navizon GPS for iPhoneNavizon, who released a third-party software GPS solution for the iPhone a few months ago, announced today that it is offering a new, free version of it's software. The previous version of the Navizon software offered a 15-day free trial after which the software expired. The new version will switch to a 'Lite' mode after the trial expires and allow users to continue enjoying Navizon's GPS services, albeit in a dumbed-down fashion.

The new Navizon Lite is basically a less accurate version of the fully-functional Navizon software. Instead of providing what Navizon claims to be the 10-30 meter accuracy of the full version of Navizon, Navizon Lite provides approximately 1500 meter accuracy (roughly a mile).

Free Version of Navizon GPS for iPhoneEssentially, Navizon Lite is Navizon without WiFi positioning. This limits Navizon's positioning abilities to cellular tower triangulation, thus the reduced accuracy. While not terribly useful in urban settings, the lite version of the Navizon software may do the trick for those of you who just need basic location services when traveling.

The lite version of Navizon also omits the "trail" feature that is included in the full version of Navizon, which tracks your iPhone as it moves. However, the buddy list/locator and "rewards" features of the full version are still included. Navizon Lite is also available for Windows Mobile, Symbian/Nokia and Blackberry devices.


Labels: ,

Read more...

 Tip: iPhoneDrive Brings Disc Mode to iPhones


iPhoneDrive ($9.95), from Ecamm Network, allows you to use your iPhone for file storage, something you can't do with Apple's iPod/smartphone combo out-of-the-box, as there's no disk mode for iPhones like there is for iPods.Tip: iPhoneDrive Brings Disc Mode to iPhones

Launching iPhoneDrive brings up the utility’s browser window and toolbar. It is from there you can transfer files and folders back and forth between your Mac OS X computer and iPhone.

There are two ways to perform transfers to an iPhone: Drag and drop content from the Mac Desktop or a Finder window into the iPhoneDrive browser or click the "Copy To iPhone" button on the toolbar.

To do the reverse, you can either click the "Copy From iPhone" button on the toolbar to move highlighted files or folders to a location of your choosing on the computer; drag content directly from the iPhoneDrive browser window into a Finder window or onto the Desktop; or simply double-click a file to download it to your Documents folder.

With iPhoneDrive, you can also create folders on and delete files or folders from your iPhone.

You can't view content you've transferred from your computer on the iPhone with iPhoneDrive, however, as the software is for storage purposes only.


Labels: ,

Read more...

 Hackers Regain Access to iPhone Under Firmware 1.1.1


Erica Sadun of TUAW, well known in the iPhone community for "Erica's utilities", has been liveblogging her attempt to replicate the success of two iPhone hackers, named "dinopio" and "Edgan", who have recently regained access to the full file tree of the iPhone through a bit of upgrade trickery. The latest update show that Erica has acheived similar success, proven by screen shots she has posted.

Evidently, access was regained by symbolically linking (symlinking) a portion of the iPhone's filesystem prior to an upgrade from firmware version 1.0.2 to version 1.1.1. The symlink in question is created by backing up the phone's Media directory and then symlinking the filesystem root to the Media directory.

Once the symlink is in place and the iPhone is upgraded, access is gained to the entire file tree using iPHUC (the iPhone Utility Client). In Sadun's tests, read and write access is tested and working, and a copy of the new Mobile Music Store application (MobileStore.app) has been pulled down.

The hope is that this latest development will give hackers the access they need to once again re-open the iPhone to third party applications and even once again provide a SIM unlock for those who want to use the iPhone with a GSM service provider other than AT&T.

The cat and mouse game continues ...

Labels: ,

Read more...

 iPhone Firmware 1.1.1 Update Video Walkthrough


Apple has a video tour of the new features in iPhone 1.1.1. We covered them in our Firmware Update Changelog earlier, but the video gives you a quick tour of the new features to enable you to see whether it's worthwhile or not for you to upgrade in this limbo-time when third-party hacks and apps aren't quite working yet. [Apple]
[Via http://gizmodo.com]

Labels: ,

Read more...

 iPhone Firmware Version 1.1.1 Released, Update Wisely


iPhone Firmware Version 1.1.1 Released, Update WiselyApple's newest update for the iPhone, firmware version 1.1.1 has been released and includes a long list of feature additions, bug fixes, and security enhancements. As always, the new firmware can be installed on your iPhone via the iPhone "check for updates" button in iTunes.

As previously reported, Apple has made it quite clear that applying the update to a modified or "hacked" iPhone can cause permanent and irreparable harm to the device which will NOT be covered under and Apple warranty. if you have performed ANY type of unauthorized modifications to your iPhone (custom ringtones, jailbreaking, custom software, and especially unlocking), make sure to read on and/or research the new update before applying it.

Users who unlocked their iPhone via any of the many available methods (iPhoneSIMFree, iUnlock, AnySIM) should simply not install the update at this time. Hold tight and wait for more info to be revealed about the consequences of updating an unlocked phone and the proper method of applying an update.

If you have performed non-unlock related modifications, such as jailbreaking and the installation of 3rd party software, initial reports are that performing a restore of your iPhone before updating is safe. These are initial reports of course, so update at your own risk.

Of course, during the restore process you'll be erasing any third party software or other custom modifications you've made to your iPhone. In fact, you'll be erasing the phone and restoring it to it's factory software condition. Make sure to back up anything on the iPhone you'll miss before doing so.

Once you have updated, you'll have to wait for new versions of software like Installer.app, iFuntastic, or iBrickr before you can re-modify your iPhone under the new software. That said, should you have fallen in love with your mods - wait.

Labels: ,

Read more...

 Free iPhone Software Unlock is Here - iUnlock


"You wanted it, we have it. Enjoy your free iPhone."

Such was the announcement on the iPhone Dev Wiki team's website when their ultimate goal - a full software unlock of the Apple iPhone - was acheived. Simple as that.


Hot on the heels of the troubled release of the iPhoneSIMFree Unlock solution, the iPhone Dev Wiki team - who has been responsible for virtually every publically available innovation involving the iPhone and it's underlying OS (filesystem access, ringtones and customization, third party applications, etc) - have released their solution which performs a similar task. Dubbed iUnlock, their solution is available free of charge, unlike others. In fact, the team has even made the source code publically available.

Early reports indicate that while slightly more complex than the iPhoneSIMFree solution, iUnlock definitely works. From a complexity standpoint, the good news is that a member of the unlock team has indicated that a GUI version of the unlock software should be available soon and will greatly simplify the process for those of you with fat fingers.

For now, the detailed instructions to complete the unlock are available via the Official iPhone Unlock Guide. Included are links to all required software to complete the unlock.

Labels: ,

Read more...

 iPhone Unlocking Software Release Blocked by Legal Warnings


It was announced yesterday that a second company was preparing to provide software that would unlock the Apple iPhone and allow it to be used on any GSM network worldwide. The announcement, which came from mobile phone unlocking company UniquePhones, promised the software would be available to consumers today (August 25th), for a price between $25 and $50.

The initial team, which proved their iPhone unlocking software works, iPhoneSIMfree.com has not yet publically released their software. They have, however, unlocked phones for press outlets. Their delay in releasing would have made the Uniquephones solution the first publically available unlocking tool.

Unfortunately, alleged legal warnings from AT&T via a law firm out of Silicon Valley, have seemingly put a halt on the process. According to the project's blog,

It is now 12N EST – the time when we said we would be offering iphone unlocking software to our customers.

We have the software. It works. And we are ready to go.

Seems AT&T is a bit annoyed at the idea. A middle of the night phone call from a Silicon Valley law firm is slowing down the release of the software to you.

Stay tuned.

It might come as no surprise that Apple or AT&T would want to put the brakes on a publically available unlock, although it is not entirely clear on what legal grounds they would block the unlock. Laws on iPhone unlocking vary widely from country to country and state to state and have historically been difficult to enforce.

The Uniquephones iPhone unlocking team has indicated they will issue a press release later today. Stay tuned for more information.

Labels: ,

Read more...

 iPhone Full Software Unlock is Here, Working, Confirmed


We all knew it was only a matter of time. For some it has taken longer than expected while others are shocked at how rapidly hackers were able to tear apart the reportedly impenetrable Apple defenses on the iPhone. Regardless of your level of surprise, the fact of the matter is that the iPhone is now fully unlocked, and the iPhone can be used on any GSM carrier anywhere in the world.

iphone and mobile

The unlock is here, without question, though it might not be from the source most people were expecting. The iPhone Dev Wiki team, which has been behind the vast majority of progress in hacking the iPhone, and who have been knocking at the full unlock door for weeks were not behind the unlock. Though it's unclear whether or not their efforts contributed to the unlock (it is incredibly likely that it did), the unlock announcement came from another source.

Today at high noon, Engadget posted a report offering extensive, detailed proof that a team of hackers out of iPhoneSIMfree.com had acheived a full, software based unlock of the Apple iPhone. In the demonstrations provided to Engadget, the iPhone was unlocked using the iPhoneSIMfree.com software. Subsequently, a T-Mobile SIM card was inserted into the iPhone and re-registered on the T-Mobile network.

The whole process reportedly took only minutes and was relatively painless.

For the most part, the unlocked on the iPhone is pretty much the same as a locked iPhone on AT&T's network. There are a few added options for carrier selection and EDGE settings. Of course, visual voicemail doesn't work, as this feature requires AT&T's service.

Unlike the Dev Wiki team which has been making all of their hacks and advancements publically available, the iPhoneSIMfree.com team is not releasing their unlock software, at least not at this point. The presumption is that they'll be trying to make money off their acheivement, and who can blame them?

We'll stop rehashing all of this at this point. Head to Engadget via the link at the bottom of this article for all the details, pics, video, and more.

[via Engadget]

Labels: ,

Read more...

 TurboSIM Unlocked iPhones For Sale in Hong Kong


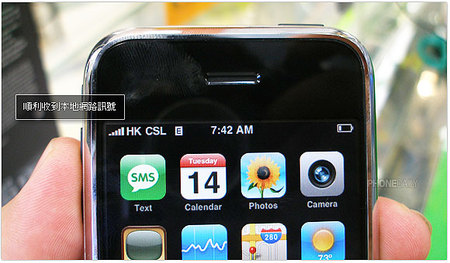
With last week's development of the TurboSIM unlocking method, it was likely only a short matter of time before seeing "unlocked" iPhones for sale for use with other providers both inside and outside the United States. As reported by PhoneDaily, this is now the case in Hong Kong.

unlocked iphone on hong kong csl

The following video shows a TurboSIM unlocked iPhone being used to make calls on Hong Kong'sCSL network.


Though not a true unlock, the TurboSIM method is by far the best unlocking method available thus far. Technically a hardware unlock, a TurboSIM is a secondary SIM card that piggy backs onto your existing SIM card. In this unlocking method, vital AT&T SIM card method is placed onto the TurboSIM and inserted into the phone with the third party carrier's SIM card. Once this is completed, the iPhone can successfully perform SIM card checks for the AT&T information it wants to find, while utilizing another carrier's SIM when initiating calls and data transmissions.

Using this method, iPhone owners should be able to use the iPhone successfully for calling and data transmissions on any GSM/EDGE service provider. Provided this is the case, we'll likely see more of these phones sold for use in other high-demand markets such as the UK and Canada.

While customers eagerly on other carriers eagerly await a true software unlock of the iPhone, this may provide another option for those who just can't wait any longer.

These unlocked phones are reportedly selling for $699 (4GB) model and $899 (8 GB model).

Labels:

Read more...

 The iPhone Hacking Kit, step by step


iphoneterminal.jpgFor better or worse, Apple designed the iPhone to be a completely closed system. That is, you can’t add new applications to it, and even some seemingly “normal” cell phone features - like the ability to add custom ring tones - are locked up. Or are they?

Thanks to an extremely well-organized group of very talented hackers, you can crack into your iPhone and make all sorts of changes and modifications. The iPhone hacking effort has been a Herculean task, but the progress that’s been made in a reasonably short amount of time is very impressive.

In the month since the iPhone shipped, hackers have released code that allows you to perform all sorts of modifications, from installing custom ringtones, to adding new applications such as a screen capture program, and a Nintendo emulator.

Hacking the iPhone is not a complicated process, but it does take time, usually 30 to 45 minutes, and some special software and bits of code, which we’ve gathered up for you. Best of all, once your phone is hacked, you can very easily install additional third party apps as they’re released. In this article, we’ll walk through all of the steps required to hack your iPhone and install third party applications and options.

(If you want to know the story behind this story, read Christopher Breen’s blog entry at Macworld.com.)

Detailed (and we’re not kidding) instructions after the jump. If you’re faint of heart, begone!

Why should you hack your phone?

Because it's there.

For the most part, there's not a huge reason to hack your iPhone yet. Adding custom ringtones is probably the best reason to do a little iPhone hacking. Capturing screenshots of your iPhone is another good excuse to hack it (you'll see screenshot examples later).

But currently, there's not a "killer app" for iPhone hacking. The Nintendo emulator is cool-looking, but is somewhat unplayable due to the iPhone's lack of real buttons. At this point, the only real reasons to hack your iPhone are:

  • It's fun. You get to learn some stuff about the inside of your phone, and possibly learn some cool Unix stuff along the way.
  • It will make your iPhone look different and unique. Once you have a couple of additional apps on there, other iPhone users will take pause when they see your phone.
  • You'll be prepared for future third-party releases. Once your iPhone is hacked, it's very simple to add additional applications as they become available. Development is proceeding very quickly - the Nintendo emulator was available just a week after the iPhone hacker development tools were posted.

Hacking your iPhone requires an Intel Mac, a set of files and the iPhone Hacking Kit, which you can download here, and some time. Unzip the iPhone Hacking Kit folder and place it on your Desktop. It must be on the Desktop for these instructions to work as they are printed here. Finally, your Mac and iPhone need to be connected to the same Wi-Fi network.

Before we begin, though, we must issue the obligatory warnings: it is theoretically possible to screw up your phone. However, at any time, you can use iTunes to restore your phone to its original state, so you don't have to worry about completely breaking your phone. The worst that will happen is that you'll lose some time. That said, if taking things apart makes you nervous and uncomfortable, then what we're going to do here probably isn't for you.

We'll be performing most of our hacks through the Terminal application on your Mac. Just type carefully and proceed slowly and you'll be fine. And don't worry, a single typo will not trash your whole phone.

What we're going to do

Before we get started, let's take a high-level look at exactly what we mean when we say we're going to "hack the iPhone." Our goal is to open up a communications channel that will let us add new, executable applications to the iPhone. The iPhone is a communications device, so one would think that it would be easy to communicate with it, but because Apple designed it to be unmodifiable, finding a way to talk directly to the phone is not simple.

Yes, the phone has a Wi-Fi connection, a cellular radio, and Bluetooth, but it doesn't actually include any software that can use these features for file transfer, and there's no way to hack into any of those particular connections.

However, it does include a serial port and a cable, and it knows how to talk to iTunes through this connection. This, then, will be the initial method for talking to the iPhone. Thanks to some clever software, we'll begin by breaking the phone out of the "jail" that Apple has put it in.

Jailbreaking works by intercepting the communication that is supposed to happen between the iPhone and iTunes. Once intercepted, a channel is open to the computer's OS, and we can use that channel to install software. However, this channel requires a direct connection to your Mac (through the iPhone's USB cable) and while your phone is "jailbroken" you can't sync. As such, it's not a viable long-term solution for hacking the phone.

So, our first task after the phone has been broken open will be to install an SSH tool. SSH stands for "secure shell" and is a standard Unix tool for issuing commands to any computer that's running Unix. And, since your iPhone is built on an OS X variant, it's a Unix computer.

Next we'll install some additional utilities, including some file transfer utilities, and then finally we'll put the phone back in jail. That is, we'll return it to its normal state that allows it to sync with iTunes through its serial cable. However, with the SSH and file transfer utilities installed on the phone, you'll now be able to talk to the phone from any Mac terminal window via the phone's Wifi connection - just as you can talk to any other Mac or Unix machine this way. We'll use this channel to install a Terminal application and screen shot utility.

Let's get started.

Get out of jail free

In the iPhone Hacking Kit that you downloaded, you should find an installer for iFuntastic. Double-click this installer to install iFuntastic in your Applications folder. This is the program we will use to jailbreak your phone.

Once it's installed, do the following:

1. Reboot your Mac, just to be safe. You don't want iFuntastic crashing during this process.

2. Make sure your iPhone is on, then plug it into your Mac using the usual cable.

3. After iTunes launches, quit it.

4. Double-click iFuntastic to launch it.

5. On the left side of the iFuntastic window there is a button called Prepare. Press it now.

6. Click the Jailbreak button at the bottom of the window.

7. On the next page are six steps. Follow them very closely.

8. If all goes well, you will see this page:
figure2.jpg

If the jailbreak fails, don't panic, just try it again until it works.

9. Now hide iFuntastic by pressing Command-H. We'll be returning to it later.

Your iPhone won't look or function any differently once it's out of jail. The only change is that when you plug it in it won't sync with iTunes. Don't worry, we'll re-jail it when we're finished to get it back to normal.

Now we're ready to exploit our newfound connection to our phone.

Not your average bear

As mentioned earlier, our ultimate goal is to end up with an iPhone that has software on it that can communicate with our Mac via a normal Wifi connection. With the phone jailbroken and tethered to the Mac, we have a communications channel which we will now use to install an SSH application called Dropbear. From here on out we'll be working extensively with the Terminal application, so open it now. By default, it's located in Applications>Utilities.

Once Terminal is launched, you need to change to the iPhone Hacking Kit directory. In terminal type cd followed by a space, and then drag the iPhone Hacking Kit folder into the terminal window. Then press Return. Your terminal window should now say something like:

Your Mac:~/Desktop/iPhone Hacking Kit yourmac$

Located in the iPhone Hacking Kit folder is a copy of iPHUC, the iPhone Utility Client. Run it now by typing

./iPHUC

and then pressing return.

You should see:

>> By The iPhoneDev Team: nightwatch geohot ixtli warren nall mjc operator
initPrivateFunctions: this is still not clean.
Architecture: i386
AMDeviceNotificationSubscribe: 0
CFRunLoop: Waiting for iPhone.
notification: iPhone attached.
AMDeviceConnect: 0
AMDeviceIsPaired: 1
AMDeviceValidatePairing: 0
AMDeviceStartSession: 0
AMDeviceStartService AFC: 0
AFCConnectionOpen: 0
AFCPlatformInit: (no retval)
notification: Entering shell in Normal Mode.
shell: Entering loop.
(iPHUC) /:

We are now in a shell that's talking directly to the iPhone, just like any other type of shell that you might normally run in Terminal. This one, though, knows how to communicate through the jailbreak connection that we've established through the serial cable.

Now we need to make one little change to the phone. Do this by typing:

setafc com.apple.afc2

After pressing return, iPHUC might respond with this error:

InvalidResponse
AMDeviceStartService AFC: -402653165
AFCConnectionOpen: 0

If it does, then quit iPHUC by typing exit, then run iPHUC again by typing ./iPHUC.

Now enter setafc com.apple.afc2 again, and press return. You should now see:

AMDeviceStartService AFC: 0
AFCConnectionOpen: 0

If you see the Invalid Response message, quit iPHUC and try again. When things are working, you should see something to the effect of:

AMDeviceStartService AFC: 0
AFCConnectionOpen: 0

Don't worry about the numbers. In some cases, you might have to actually quit Terminal completely and restart. Keep going until the command completes without the Invalid Response error generating.

To ensure that everything is working properly, type ls and press return. If you're used to using Terminal, you'll recognize ls as the List Directory Contents command, and sure enough, you should see a directory listing:

.
..
Applications
Library
System
bin
cores
dev
etc
iTunes_Control
mach
private
sbin
tmp
usr
var

These are the contents of the iPhone's root directory and as you can see, they look very much like a standard OS X root directory. If you don't see this directory, quit iPHUC and try again.

Now we need to retrieve two files from the iPhone. Later, we'll see what these are for.

In the Terminal, enter
getfile /System/Library/LaunchDaemons/com.apple.update.plist com.apple.update.plist.original
and press return. iPHUC should respond with:

remote: /System/Library/LaunchDaemons/com.apple.update.plist
local: com.apple.update.plist.original
AFCFileRefOpen: opening remote path '/System/Library/LaunchDaemons/com.apple.update.plist'
AFCFileRefRead: reading 489 bytes into buffer
getfile: Writing file to local path 'com.apple.update.plist.original'
getfile: Transfer successful.

If you look in your iPhone Hacking Kit folder on your Mac, you should see a new file called com.apple.update.plist.original. This is a copy of a preference file that we just pulled off of the iPhone and renamed.

Now enter getfile /usr/sbin/update update.original and press return.

Again, you should see the Transfer successful message, and another file will appear in your iPhone Hacking Kit folder. This time, we grabbed the update daemon from the iPhone. This is a small application that gets executed when the phone boots. We renamed the daemon update.original when we saved it to the local drive. The reason for all this will become clear shortly.

Now it's time to put Dropbear, our SSH tool onto the iPhone. Issue the following commands. After each one you should see "Transfer successful". If you don't, then double-check your typing and try again. You'll need to replace [username] with your user name.

Next, enter mkdir /etc/dropbear

This creates a directory called dropbear in the /etc directory.

Using the Putfile command, you'll need to move several files from your iPhone Hacking Kit onto the iPhone. You'll do this by typing putfile and pressing space, then dragging and dropping the file from the finder onto a Terminal window, then typing a space, then typing the path of the destination directory.

For example, for the first entry the end result would be:

putfile /[path to hacking kit]/sh /bin/sh

File to Drop Destination to type
sh /bin/sh
chmod /bin/chmod
dropbear /usr/bin/dropbear
au.asn.ucc.matt.dropbear.plist /System/Library/LaunchDaemons
dropbear_rsa_host_key /etc/dropbear
dropbear_dss_host_key /etc/dropbear
chmod /usr/sbin/update
com.apple.update.plist.hacked /System/Library/LaunchDaemons/
com.apple.update.plist

We've done several things here. First, we put a copy of a shell application called sh into the /bin directory on the phone. Ultimately, we will need a shell application to be able to communicate with the phone from the Mac terminal, so that's why we're installing it now.

Next, we placed a copy of a program called chmod in the /bin directory. All files in a Unix operating system have permissions attached to them, and chmod is a program that lets us alter permissions. We'll use chmod to make the applications that we install executable.

Next we installed Dropbear in the /usr/bin directory. This is the SSH program that we want the phone to run. After that, we installed a plist with a long name in the /System/Library/LaunchDaemons directory.

We placed two host key files in the /etc/dropbear directory that we made earlier. SSH needs these files to perform its secure, encrypted transfers.

Finally, we placed another copy of chmod in the /usr/sbin directory, but this time we named the resulting file update. As you'll recall, earlier we pulled a copy of update off of the iPhone. We're now writing over the update app that's on the iPhone with a chmod app. You'll see why in a sec. We also installed a plist in the com.apple.update directory.

So, we've copied Dropbear onto the phone, as well as some utility files that it needs, but we've also done something else. Before an application can be run, its permissions must be set to executable, which we can do with the chmod application that we installed. The problem is, how do we get chmod to run on our Dropbear application because right now, we have no way to execute a program.

In the old days of iPhone hacking (that is, the morning of June 30, 2007 at roughly 10ish) you used special tools to pull off an image of the iPhone's contents. Then you manipulated that image on your Mac, installing software and changing permissions, and put the whole thing back on. This was difficult and time-consuming, which is why an enterprising hacker named Nervegas came up with a new trick.

When your iPhone is booted, it automatically runs certain applications called daemons. The update daemon is one of those. As you'll recall, we made a copy of update early on. You've now replaced the update daemon on the phone with a copy of chmod. When you reboot your phone, it will blithely execute update, just as it's supposed to, with no idea that it's actually running chmod. The com.apple.update.plist.hacked file that we installed (but named com.apple.update) contains the parameters necessary for chmod to alter the preferences of our Dropbear application to make it executable.

Once Dropbear has been made executable, it will run any time the phone is powered on. So:

Now turn your phone off, and then turn it back on. Because you're still jailbroken, iTunes will launch and then quit. When the phone is back up and running, turn it off and on again. Again, iTunes will launch and quit. You have now rebooted your phone twice. The first time, our Trojan chmod application modified the permissions of Dropbear. The next time, the now-executable Dropbear should start running, and voila! You'll have an ssh daemon running on your iPhone!

After the phone has rebooted the second time, we need to test to see if ssh is running. Any time you want to SSH into your iPhone, you must know the phone's IP address. On the phone, press Home, then Settings, then Wi-Fi, then look at the details for the network that you're connected to. You'll find the IP address in there.

  1. In the Terminal window, type exit, to quit iPHUC.
  2. Type ssh root@[iPhone's IP address]. For example ssh root@192.168.1.14.

The iPhone should respond with something like:

The authenticity of host '192.168.1.14 (192.168.1.14)' can't be established.
RSA key fingerprint is 5a:e4:fa:de:62:f6:9b:96:7f:3b:57:b1:76:21:77:d6.
Are you sure you want to continue connecting (yes/no)?

Type yes and hit return. When it asks for a password, enter dottie. By default, all iPhones have a password of dottie.

You should see a prompt like this:

-sh-3.2#

Congratulations! You've just installed an ssh client and ssh'd to your iPhone!

  1. Enter ~. To exit ssh. If it continues to display the ssh prompt, try again.

Back to normal

Now we need to restore some things on the phone to normal. As you just learned, to get this all to work, we had to replace the update daemon with chmod. Now we need to put update back where it was.

Launch iPHUC by typing ./iPHUC in the Terminal and then enter these commands (each of them on a single line, despite the fact that on this web page the information breaks over multiple lines):

putfile /Users/[user name]/Desktop/iPhone\ Hacking\ Kit/com.apple.update.plist.original /System/Library/LaunchDaemons/com.apple.update.plist

putfile /Users/[user name]/Desktop/iPhone\ Hacking\ Kit/update.original /usr/sbin/update

Those two commands restore the update daemon.

Your phone now has an ssh client on it, and a password known by anyone who's reading this article (as well as a bunch of really talented hackers). The odds of someone looking for an iPhone to hack in a public place are small, but if you really want to be secure, you can change your password.

To change the password of your phone:

  1. In the Terminal, exit iPHUC by typing exit.
  2. At the prompt, enter perl-e 'print crypt("mypassword","xx");'

Substitute your desired password for mypassword, and enter any two characters in place of XX.

Terminal will display an encrypted version of your password.

  1. In the iPhone Hacking Kit folder, you'll find a file called master.passwd.original. Open this in TextEdit and replace both the mobile and root passwords with the encrypted text.

For example, if you generated the following password in step 2: XXVeA.Z.EZ6FA

Then, in the master.passwd.original file, you would change this:

root:XUU7aqfpey51o:0:0::0:0:System Administrator:/var/root:/bin/sh

to this:

root: XXVeA.Z.EZ6FA:0:0::0:0:System Administrator:/var/root:/bin/sh

and this:

mobile:/smx7MYTQIi2M:501:0::0:0:Mobile User:/var/mobile:/bin/sh

to this:

mobile: XXVeA.Z.EZ6FA:501:0::0:0:Mobile User:/var/mobile:/bin/sh

  1. Choose File > Save As and save the document back into the iPhone Hacking Kit folder as master.passwd.
  2. Because TextEdit tends to add .txt extensions, select the file, choose File > Get Info, and get rid of the extension.

  3. In the Terminal, launch iPHUC again by typing ./iPHUC.

  4. Put the new password file on your phone with this command: putfile /Users/[username]/Desktop/iPhone\ Hacking\ Kit/master.passwd /etc/master.passwd

Now your phone is almost back to normal. But, we still have some more things to install.

SCP - The racer's edge

So far, we've been using iPHUC to manage all file transfers between the Mac and the iPhone. But we want something that doesn't require a tethered connection, so we're going to install a copy of a program called SCP. This will ensure that we can move files on and off after we've unplugged the iPhone.

Launch iPHUC and issue the following commands, once again using Putfile to move the following files into the following directories in the format

putfile [drop file here] [destination path]

File to drop Destination to type
sftp-server /usr/libexec
scp /usr/bin
libarmfp.dylib /usr/lib/libarmfp.dylib

The SCP and SFTP servers are now installed, but they need to be made executable. As you've learned, we can make a file executable by using the chmod tool. Earlier, we had to trick the iPhone into executing chmod, but now that we have ssh on the phone, we can simply ask the phone to execute chmod.

Enter ssh root@[iPhone's IP address]

When prompted, enter your password, you will then be presented with an ssh prompt: -sh-3.2#

Now the Terminal window is acting as a terminal directly to the iPhone. In other words, any commands we enter will be executed by the phone. Tell the phone to execute chmod to change the permissions of the sftp-server and scp applications.

chmod +x /usr/libexec/sftp-server
chmod +x /usr/bin/scp

Now test SCP by entering scp. You should see something like this:

usage: scp [-1246BCpqrv] [-c cipher] [-F ssh_config] [-i identity_file]
[-l limit] [-o ssh_option] [-P port] [-S program]
[[user@]host1:]file1 [...] [[user@]host2:]file2

We'll use SCP shortly to install some new applications on the iPhone. But first, we need to do some cleanup.

Go directly to jail

We're just about ready to re-jail the iPhone. This will return it to its normal, sync-ready state, and will mean that you no longer have to tether it.

Before we rejail, though, we're going to move over a few more files. In iPHUC, issue the following commands in the format putfile [drop a file here] [path]

File to drop Path to type
shells /etc
bash /bin
csh /bin
rm /bin
rmdir /bin
ls /bin

We'll fiddle with those files later. For now, on your Mac, return to iFuntastic. We're ready to re-jail the phone.

Before we do, though, notice that iFuntastic allows you to add new ringtones, change the carrier logo, alter the order of icons on your home screen, and browse files. If you want to use any of these features, give them a try.

When you're finished, click the Finish button, and then the Jail button. Then, follow the on-screen instructions. This will put your phone back in jail, closing the communications loophole that we've been exploiting. iPHUC will no longer be able to talk to your phone. But that's okay, because we now have lots of other ways to do that.

After your phone has rebooted, click Done, and then give some thought to donating to the resourceful hackers who made iFuntastic possible. When you've finished, quit iFuntastic and unplug your iPhone from your Mac.

Do something useful

So far, our hacking has been limited to the "because it's there" level of satisfaction. Let's kick it up a notch and install some actual applications. We'll start with a screenshot app written by Erica Sadun. We need to transfer the screenshot app to the phone, which we'll do using the SCP application that we installed earlier.

scp [drop hacking kit screenshot here] root@[iPhone's IP]:/Applications

You'll be prompted for your phone password, and then the transfer should occur. This command sends the file screenshot to the Applications directory of the phone. You can learn more about scp by opening a new Terminal window and entering man scp.

Now we need to make the screenshot app executable.

ssh into your phone (ssh root@[ipaddress]). Because you rebooted your phone, you may want to double-check what IP it ended up with. Enter these commands:

chmod +x /bin/bash
bash

You should now see a bash prompt that looks like this:

bash-3.2#

Bash is a more versatile terminal that allows you to do a few more things.

Enter chmod +x /Applications/screenshot

Screenshot should now be executable. Let's try it. Put your iPhone on a screen that you want to capture. In your Mac's Terminal window, enter /Applications/screenshot. You should see:

About to snap screen.
Your screen shot is located at /tmp/foo_0.png

Your phone has captured a screen and stored it. Now we simply need to retrieve it, which we can do with the scp command. Open a new terminal window and enter:

Enter scp root@[iPhone's IP]:/tmp/foo_0.png /Users/username/Desktop

When prompted, enter your password. The screenshot will be captured to your desktop.

figure3.jpg

(We created a second terminal window to enter the SCP command so that we now have one terminal window that's running SSH, and another that lets us issue SCP commands.)

If you're spending a long time ssh-ing or scp-ing to and from your phone, you might find that the phone falls asleep and kills the Wifi connection. You can make it stay on longer - or indefinitely - by going to Settings > General and then changing the Auto-Lock time.

So far, we've been using the Mac's terminal to control the phone. Let's install a terminal app that we can use on the phone itself.

Enter scp -r [drop Terminal.app from Hacking Kit here] root@[ip address]:/Applications/Terminal.app to transfer the terminal application to the phone. We have to add -r to the scp command because, technically, the Terminal app is a directory.

Now we need to make the app executable. SSH to your phone and then enter:

chmod +x /Applications/Terminal.app

Now restart your phone. Once it's up, you should see a new icon on your home screeen!

figure4.jpg

Press Terminal, and the terminal app will launch. Any commands that you've been issuing through ssh you can now do directly on the phone. For example, let's launch the bash shell. In the iPhone Terminal, enter bash and press return.

figure5.jpg

Just before we put the phone back in jail, we copied some additional commands to the bin directory. Let's make three of them executable. In the iPhone terminal, enter:

chmod +x /bin/rm
chmod +x /bin/rmdir
chmod +x /bin/ls

RM is a remove command that let's us delete files, while rmdir lets us delete directories. LS is the list directory contents command that we used earlier. We'll fiddle with these again later.

Bash is a much better shell than the default shell that the Terminal executes. So, if you find yourself unable to execute certain basic commands in Terminal, then try launching bash.

Let's do a little iPhone customization. Personally, I don't find the Stocks application to be very useful, so let's remove it. Because we might later have some great windfall that would make the Stocks app more handy, we'll back it up first, so that we can always put it back later.

In your Mac's Terminal window, enter the following:

scp -r root@[iphone IP address]:/Applications/Stocks.app /Users/[your user name]/Desktop

This will copy the Stocks program to your Mac desktop. Now enter the following commands (you can do this either via ssh on your Mac, or directly into the Terminal on your phone). Be sure to enter the path exactly as it is shown here, as this command will remove an entire directory, and you don't want to accidentally remove your entire Applications directory:

rmdir -rf /Applications/Stocks.app

Now reboot your phone. When it powers back up, you should find that the Stocks application is gone. If you ever want to put it back, just use SCP to transfer the copy that you saved to your desktop back to your /Applications directory. Then use chmod to make /Stocks.app/Stocks executable. Reboot the phone and it will be right back where it started.

All of this should be enough to get you started. You've got a good assortment of commands and an understanding of how to move things on and off your phone. As more apps are developed you can use SCP to transfer them to your phone, and CHMOD to make them executable.

Note that, with the next update, Apple could wipe out all of your changes. If this happens, you may have to re-hack the whole thing, and this may require an update to the Jailbreak application or to iPHUC. We'll try to keep you posted as these things change, and as new hacks become available.

Labels:

Read more...

 Denver man hacks thumbs for more efficient iPhone use - literally [Updated]


Iphone newsKeyboards on handheld devices and smartphones have often been debated in terms of how much work they actually let you get done. Tiny displays, limited functionality, itty-bitty keyboard buttons and now the iPhone's entirely virtual keyboard whose keys can be hard to hit for some people have given folks something to talk about. Taking matters to a level that I believe is unheard of in the technology world, however, 28-year-old Thomas Martel in Bonnie Brae (a Denver, CO neighborhood) decided to solve his large handed problem by surgically altering his thumbs to make it easier to use his iPhone.
Through a procedure called "whittling" which the North Denver News described, an incision was made into each of Martel's thumbs. The bone was shaved down, muscles were realigned and his thumbnail was modified to help bring it all together. His new 'streamlined' thumbs may look out of place in relation to his other fingers, but Martel says all the time and frustration he'll save should make the surgery pay for itself in ten to fifteen years. Of course Dr. Spars, the man who helped develop the procedure, is excited about this new avenue for plastic surgery; it aint just for makin' pretty faces anymore - now you too can have your very own iPhone-optimized thumbs for the low, low price of... well the North Denver News article doesn't say. My guess on the procedure's price though is somewhere in the range of 'a heckuva lot', given that time and frustration are tough things to add up over fifteen years. Depreciating values and market shifts in the value of frustration alone are enough to make one's head spin.

What about you, TUAW readers? Anyone planning on hacking their thumbs for more better iPhone usage? How about whittling out a spot in a thigh so the phone rests a little better? I'm thinking about bypassing an armband case altogether and simply chopping out a chunk of my arm for taking the iPhone running. Maybe I'll see what Dr. Nick's prices are like this week.

[Update 2: As some commenters have pointed out, this story has finally been officially claimed as satire by North Denver News. I guess the same ol' lesson that I have had to learn myself applies: if a news outlet typically known to print true stories (no matter how quirky they may be) tries to pull off satire, they need to let readers know up front (i.e. - a tiny link that's added at the bottom of the article just above a paid advertisement post-publication doesn't quite cut it). In summary: no one had their thumbs surgically altered to work with an iPhone more efficiently; nothing more to see here folks.]

[Update: As these stories sometimes go, it appears that this might not all be true. Richard Martin at InformationWeek did some digging for Dr. Spars and James Benfly, the author of the article at North Denver News. Benfly hasn't returned any of Martin's calls, and Martin finds it a bit suspicious that there is no phone book listing for a Dr. Robert Fox Spars in the Denver area. While I too found it a little odd that Denver North News is using what looks like a default template for the open source Joomla software to pXuất bản Bài đăngower their site, a friend did some checking and found four Thomas Martel's in the Denver area. I also don't find it at all strange that Dr. Spars isn't listed in the phone book, because he could very well be listed under his practice's name which Denver North News didn't list in their article. Still, it was worth mentioning that folks are punching some potential holes in the story. I'll see if I can follow up to get any more solid information.]

Labels:

Read more...

 Apple iPhone Unlocked for Use in Europe


Not long after we updated you about a major milestone on the road to an unlocked iPhone, one which brought an unlocked iPhone ever closer, hackers have unlocked the iPhone for use in Europe.

iphone unlocked in europe

Though this does not appear to be a "true" or "full" unlock, as the method requires the creation of a new SIM card using a SIM card reader/writer, it is also more significant than previous SIM card hacks. This latest achievement has resulted in fully working (with the exception of YouTube and Visual Voicemail in some cases) iPhones operating on European carriers.

So far, users have reported iPhones working in Croatia and UK (Orange).

A tutorial featuring step-by-step instructions on how to complete the European unlock was posted by a user named Saascha on the hackint0sh forums. To complete the required steps, you'll need your iPhone, a SIM card reader/writer, an original European v1 SIM card, and a SilverCard SIM card - roughly $100 worth of ingredients (excluding the iPhone, of course).

Here is an overview of the steps to achieve the "unlock", from the hackint0sh forums:

1. iPhone
2. SIM Reader/Writer (Infinity USB Unlimited, Dynamite Programer(I used this) ,etc...)
3. SilverCard
4. V1 SIM card (U must be able to get Ki number)
5. Download - http://simemu.gsmhosting.net/SIM_EMU_6.01_CFG_v2.1.zip
- http://www.kinforce.com/down/kinforc...rsim/ws109.zip

Getting IMSI,ICCID & Ki number from your SIMs

Step 1 - Your(V1)SIM

1. Put your carrier SIM card in programer
2. Run Woronscan
3. Click on "Tasks" tab then on "IMSI select" u will get a IMSI number, write it down.
4. Click on "Task" tab then on "ICC select" u will get a ICCID number, write it down.
5. Click on "Tasks" tab then on "Ki search", in pop-up window just click "Search", and wait,Ki extraction has began.(I was waiting for mine 40 min ) When u get it, write it down.

Step 2 - Getting IMSI from AT&T SIM card which came with an iPhone

1. Put your AT&T SIM card in programer
2. Click on "Tasks" then on "IMSI select" u will get a IMSI number, write it down.
3. Close Woronscan
4. Remove SIM from programer

Now U have all "data" to make SuperSim.

Making SuperSim

1. Download & extract: http://www.rapi****re.com/files/4693....01_iPhone.rar
1.a Put your Silvercard in programer
2. Run Sim-Emu 6.01 Configurator v2.1
3. Click on Configure tab
4. Click "Read from disk" button
5. Browse to your downloaded Flash&EEPROM files, first double click on SIM_EMU_6.01_iphone.HEX and then double click on SIM_EMU_6.01_iphone_EP.HEX, now they are loaded,positions 0 and 9 are red colored,thats fine.
6. In position 0 , type in data which u got from your carrier SIM with Woronscan - IMSI,Ki & ICCID!
For ADN/SMS/FDN# type 161, 15, 4, for SMS Centre type in your carrier SMS center number.
7. Now select position 9, here type only IMSI from AT&T SIM card, NOTHING ELSE!
8. In "Config mode" check "Card" circle button
9. Click on "Write to card" button,when its done close Sim-Emu 6.01 Configurator v2.1
10. Run Woronscan again, click on "Tasks" tab then click on "IMSI select" 5 times in a row,U should get first two times AT&T IMSI rest three times your SIM IMSI,if u do u're ready to go!
11. Click on "Security" tab then on "Disable PIN1", it will ask U PIN1 ,its 1111, click OK.
12. Close Woronscan, and remove card from programer
13. http://www.mobileshop.org/usertech/simcutting.htm

Making your iPhone SuperSim compatible

Step 1
MAC - http://www.hacktheiphone.com/iphone_...dding_mac.html
WIN - http://www.hacktheiphone.com/iphone_...g_windows.html

Step 2
For already "fake activated" iPhones ,put the AT&T SIM that it came with iPhone in it or deactivation in step 12. will not work! In "Step 15" when U are filling in fileds ,for ICCID use your carrier SIM ICCID not AT&Ts! When u download a "custom activator v0.2" DO NOT PROCCED to Step 16! At this point remove AT&T SIM card from iPhone(still connected to computer),put in your SuperSim AND THEN procced to Step 16!

MAC - http://www.hacktheiphone.com/iphone_...intel_mac.html
WIN - http://www.hacktheiphone.com/iphone_...r_windows.html

As is the case with most iPhone "hacks", the process is a detailed one and should not be attempted by those with little technical experience in such matters - or the faint of heart.

Please note: depending on your location, the details listed above can potentially result in your account being blocked/cancelled by your provider. Preliminary info suggests these activities may even be considered illegal in some countries. And, as always, doing any of the above can invalidate your iPhone's warranty. Details are provided for informational purposes only.

Labels:

Read more...

 Hackers Hit Major Milestone in Unlocking the iPhone


The team behind the iPhone Dev Wiki, which has become the foremost camp of hackers attempting to unlock the Apple iPhone, has hit another major milestone in their efforts. The team released news recently that they have successfully extracted the full content of the NOR memory (from the S-Gold2).

hackers hit major iphone unlocking milestone

Although the Wiki team hasn't released the source code or the dump of the NOR memory at this point, they have released a binary which will allow others to dump the content of their iPhone's NOR memory as well.

Don't know what that means? Join the masses. The important thing is that, according to the dev wiki team, this is the "main key to achieving a true unlock". Considering that the team has already achieved 5 of the 6 self-set goals towards a fully unlocked iPhone, and have achieved a major milestone on the way to the 6th, it means they are almost there.

According to the team,

"Just a couple of days ago we managed to extract the full content of the NOR memory (from the S-Gold2), which is the main key to achieving a true unlock. Releasing this dump would be of course illegal and risky, as it contains personal information and copyrighted code. That said, we're going to release the NOR Dumper binary to enable everyone else to continue working on the iPhone's unlocking. We'll release the source code at a later date when we feel it is mature enough to do so."

Stay tuned for more info regarding the iPhone Dev Wiki team's progress, as it looks like they're getting ever closer to a totally unhinged iPhone. If you're one of the people out there waiting for an unlocked iPhone, be sure to take the time to donate to the team via their PayPal account. Even if you can only spare a few dollars, every bit helps.

Labels: ,

Read more...

 Hacked iPhone Tethers EDGE via WiFi


Mostly because it's relatively not that exciting, we've been a bit lazy in getting this story posted. The other day, via a new third party application called srelay (a SOCKS proxy server), you can now tether your iPhone EDGE connection to your laptop or desktop via WiFi. Yes, it could come in handy in a pinch, but sharing an EDGE connection with a full fledged PC isn't nearly as exciting as it would be if the iPhone were 3G.

Of course, this application and functionality is only available to you if you've hacked your iPhone. Like all other iPhone hacks, you need to start with the jailbreak hack. Once completed, you can then install srelay on your iPhone, set up a direct computer to computer WiFi connection, and off you go. The video below provides a HOWTO and demonstration of the process.


You can find lmore information on the tethering process including links to the required software here.

[via everywhere ... ]

Labels:

Read more...

 iPhone hacked for use in Australia?


iphone-aus.jpgAussie hackers have somehow managed to get an iPhone working on Australia’s Telstra mobile network, by “modifying the iPhone’s default SIM card to be recognized as an AT&T SIM, while actually containing data that allows it to be accepted by Telstra.”

We’ve yet to see actual proof of this (apparently there was a video that has since been taken down), but the preliminary results sound enticing.

CommonGate: The hack is made possible through the use of iActivator, a Mac OS X program that provides an interface for activating/deactivating your iPhone without invoking an AT&T contract or prepaid plan. The program doesn’t unlock the iPhone’s SIM, but simply unlocks the functionality of the iPhone so that an AT&T-based activation is not necessary. The tool also has the option to perform a “Jailbreak” on the iPhone, which allows files to be written to the device’s filesystem.

Labels:

Read more...


From Admin
Hello ;)